Mandatory sectors
Financial services, Energy services, Telecommunications, Healthcare, Transport, Drinking water and chemical industry, Digital infrastructure, Public services.
Recommended sectors
Small and medium-sized enterprises (SMEs) with fewer than 50 employees or a turnover of less than 10 million euros. They are not required to comply with the requirements but may follow recommended cybersecurity measures.
Depending on the scale
NIS2 is mandatory for organizations that meet any of the following criteria: 50 or more employees, or an annual turnover of more than 10 million euros.
OVERVIEW

What is the NIS2 Directive?

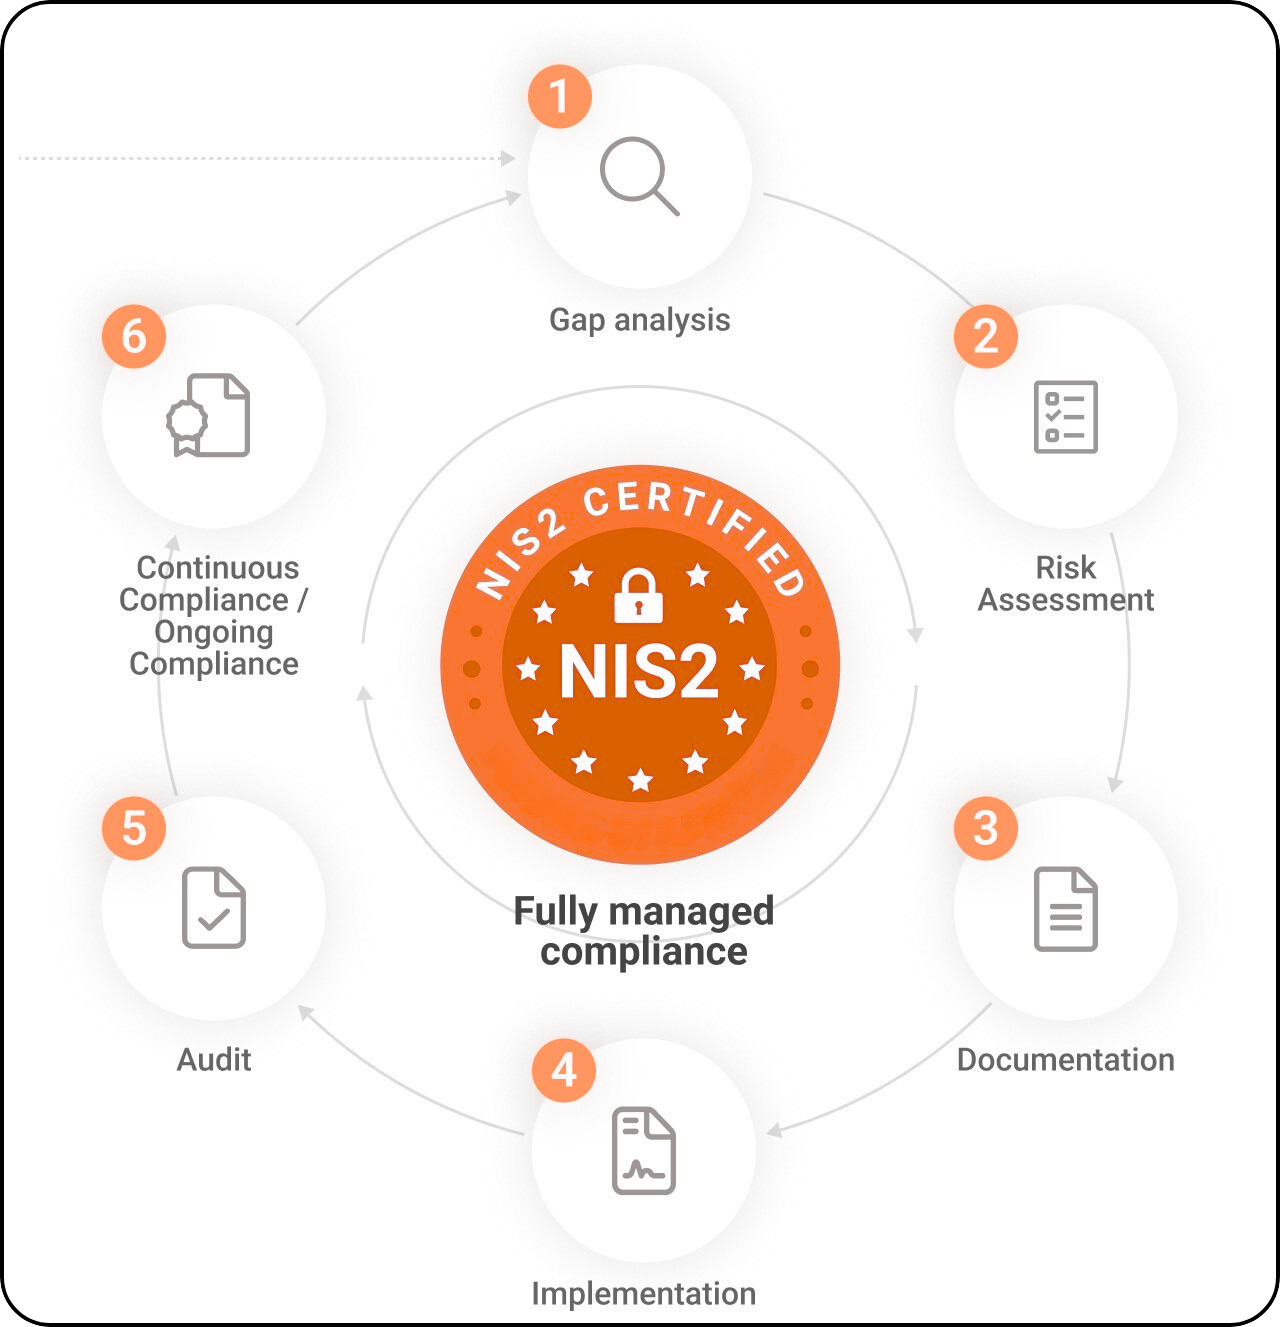
The NIS2 Directive (Directive (EU) 2022/2555) is an EU regulation that sets uniform cybersecurity standards for all member states. It updates the original NIS Directive, broadening its coverage to include more sectors and organizations. Its main goal is to align cybersecurity practices, enhance resilience to emerging threats, and enforce stricter penalties for non-compliance.

The directive follows a risk-based strategy, meaning organizations must adopt security measures that reflect the level of potential threats. It also encourages cross-border cooperation through information sharing among stakeholders and requires thorough incident reporting to improve threat detection and response capabilities.

What is the NIS2 Directive?
STEPS

Getting Started with NIS2 Compliance

Assess Applicability & Impact
Elevate Cybersecurity Awareness
Enhance Security Infrastructure
Allocate Resources Effectively
GUIDELINES

Baseline Security Measures to Meet NIS2 Standards

Risk Management Policies

Establish policies for risk analysis and information system security to effectively manage cybersecurity threats.

Incident Handling Plan

Implement a comprehensive plan to swiftly handle and respond to security incidents.

Business Continuity

Maintain up-to-date backups, disaster recovery strategies, and crisis management plans to ensure uninterrupted operations.

Supply Chain Security

Prioritize security in relationships with suppliers by assessing vulnerabilities and ensuring product cybersecurity.

System Security Lifecycle

Ensure robust security during network and system acquisition, development, maintenance, and vulnerability disclosure.

Effectiveness Assessment

Incorporate procedures to routinely evaluate the efficacy of cybersecurity risk management measures.

Cyber Hygiene Training

Promote basic cyber hygiene practices through continuous employee training and awareness programs.

Cryptographic Measures

Implement policies on cryptography, ensuring appropriate use of encryption where applicable.

Access Control & Asset Oversight

Define security procedures for employees accessing sensitive data and maintain a comprehensive asset management strategy.

Advanced Authentication

Deploy multi-factor or continuous authentication, secure communications, and encrypted emergency channels.

Network Security

Protect networks and systems by securing architecture, segmenting networks into secure zones, restricting unauthorized access, and managing remote connections.

CRITERIA

The fundamental pillars of the NIS2 cybersecurity regulation

Incident management system

Create a complete incident management system for timely detection, analysis, and response to cybersecurity events. Features should include automated alerts, incident classification, and detailed response strategies.

Supply chain security

Strengthen supply chain security by regularly auditing and evaluating third-party vendors. Ensure vendors comply with security standards and implement secure communication protocols.

Network security upgrades

Enhance network security using advanced firewall technologies, intrusion detection and prevention systems, and continuous monitoring to detect and mitigate unauthorized access or suspicious activity.

Access control mechanisms

Strengthen access control with multi-factor authentication, role-based access control, and enhanced privilege management to safeguard critical systems and data.

Data encryption

Implement comprehensive end-to-end encryption for sensitive data to ensure its confidentiality and integrity.

Cybersecurity Oversight Committee

Establish an executive-level committee to oversee cybersecurity initiatives, develop policies, and manage cybersecurity budgets.

Risk Reporting & Mitigation

Implement a structured process for management to regularly report cybersecurity risks, vulnerabilities, and mitigation efforts.

Penalties & Incentives

Create a framework of penalties for non-compliance and rewards for proactive cybersecurity risk management.

Cybersecurity Compliance Audits

Conduct regular audits to assess management’s adherence to cybersecurity policies and identify opportunities for improvement.

Management Training Program

Introduce mandatory cybersecurity training for corporate management to enhance awareness of cyber risks, best practices, and organizational policies.

Incident Reporting Platform

Utilize systems enabling suppliers, vendors, and customers to efficiently report all kinds of cybersecurity incidents.

Automated incident notifications

Set up an automated system for escalating alerts and notifications to relevant stakeholders, including regulatory bodies, within prescribed timeframes.

Incident response teams

Form specialized teams equipped with the necessary tools and expertise for prompt handling and containment of cybersecurity incidents.

Incident documentation & reporting process

Establish a detailed process for documenting incident details, responses, and post-incident analysis to enhance organizational learning and response improvement.

Incident classification guidelines

Develop clear guidelines for categorizing incidents based on severity and impact to ensure consistent reporting and effective response protocols.

Redundancy & backup

Implement data redundancy and backup strategies to maintain data availability and system resilience during and post-cyber incidents.

Business Impact Assessment

Perform thorough assessments to identify key systems and processes essential for operations during cyber incidents.

Cyber Incident Response Plan

Develop a detailed plan outlining step-by-step procedures for managing cyber incidents, including communication protocols, recovery strategies, and roles of crisis response teams.

Cybersecurity Awareness Training

Provide organization-wide training on the business continuity plan and employees’ roles in minimizing disruptions during cyber incidents.

Regular Plan Testing & Drills

Periodically test the business continuity plan and conduct simulated drills to identify gaps, improve response efficiency, and ensure ongoing effectiveness.

CONSEQUENCES

What if a company is not compliant with NIS2?

Companies failing to comply with the NIS2 Directive could face severe penalties ranging from non-monetary sanctions to substantial administrative fines. Additionally, top management personnel can be held personally accountable for non-compliance, emphasizing the significance of cybersecurity responsibility at an organizational level.
Sanctions for management
Non-monetary actions & sanctions
Administrative fines

Frequently Asked Questions (FAQ)

What is NIS2, and why is it important?

NIS2 (Network and Information Systems Directive) is an EU-wide regulation aimed at enhancing cybersecurity across member states. It establishes stronger requirements for network and information systems security, risk management, and incident reporting. NIS2 is crucial for ensuring the resilience of critical infrastructure and services in the face of growing cyber threats.

Let’s get started

We look forward to discussing the best solution for deploying your projects in the cloud.